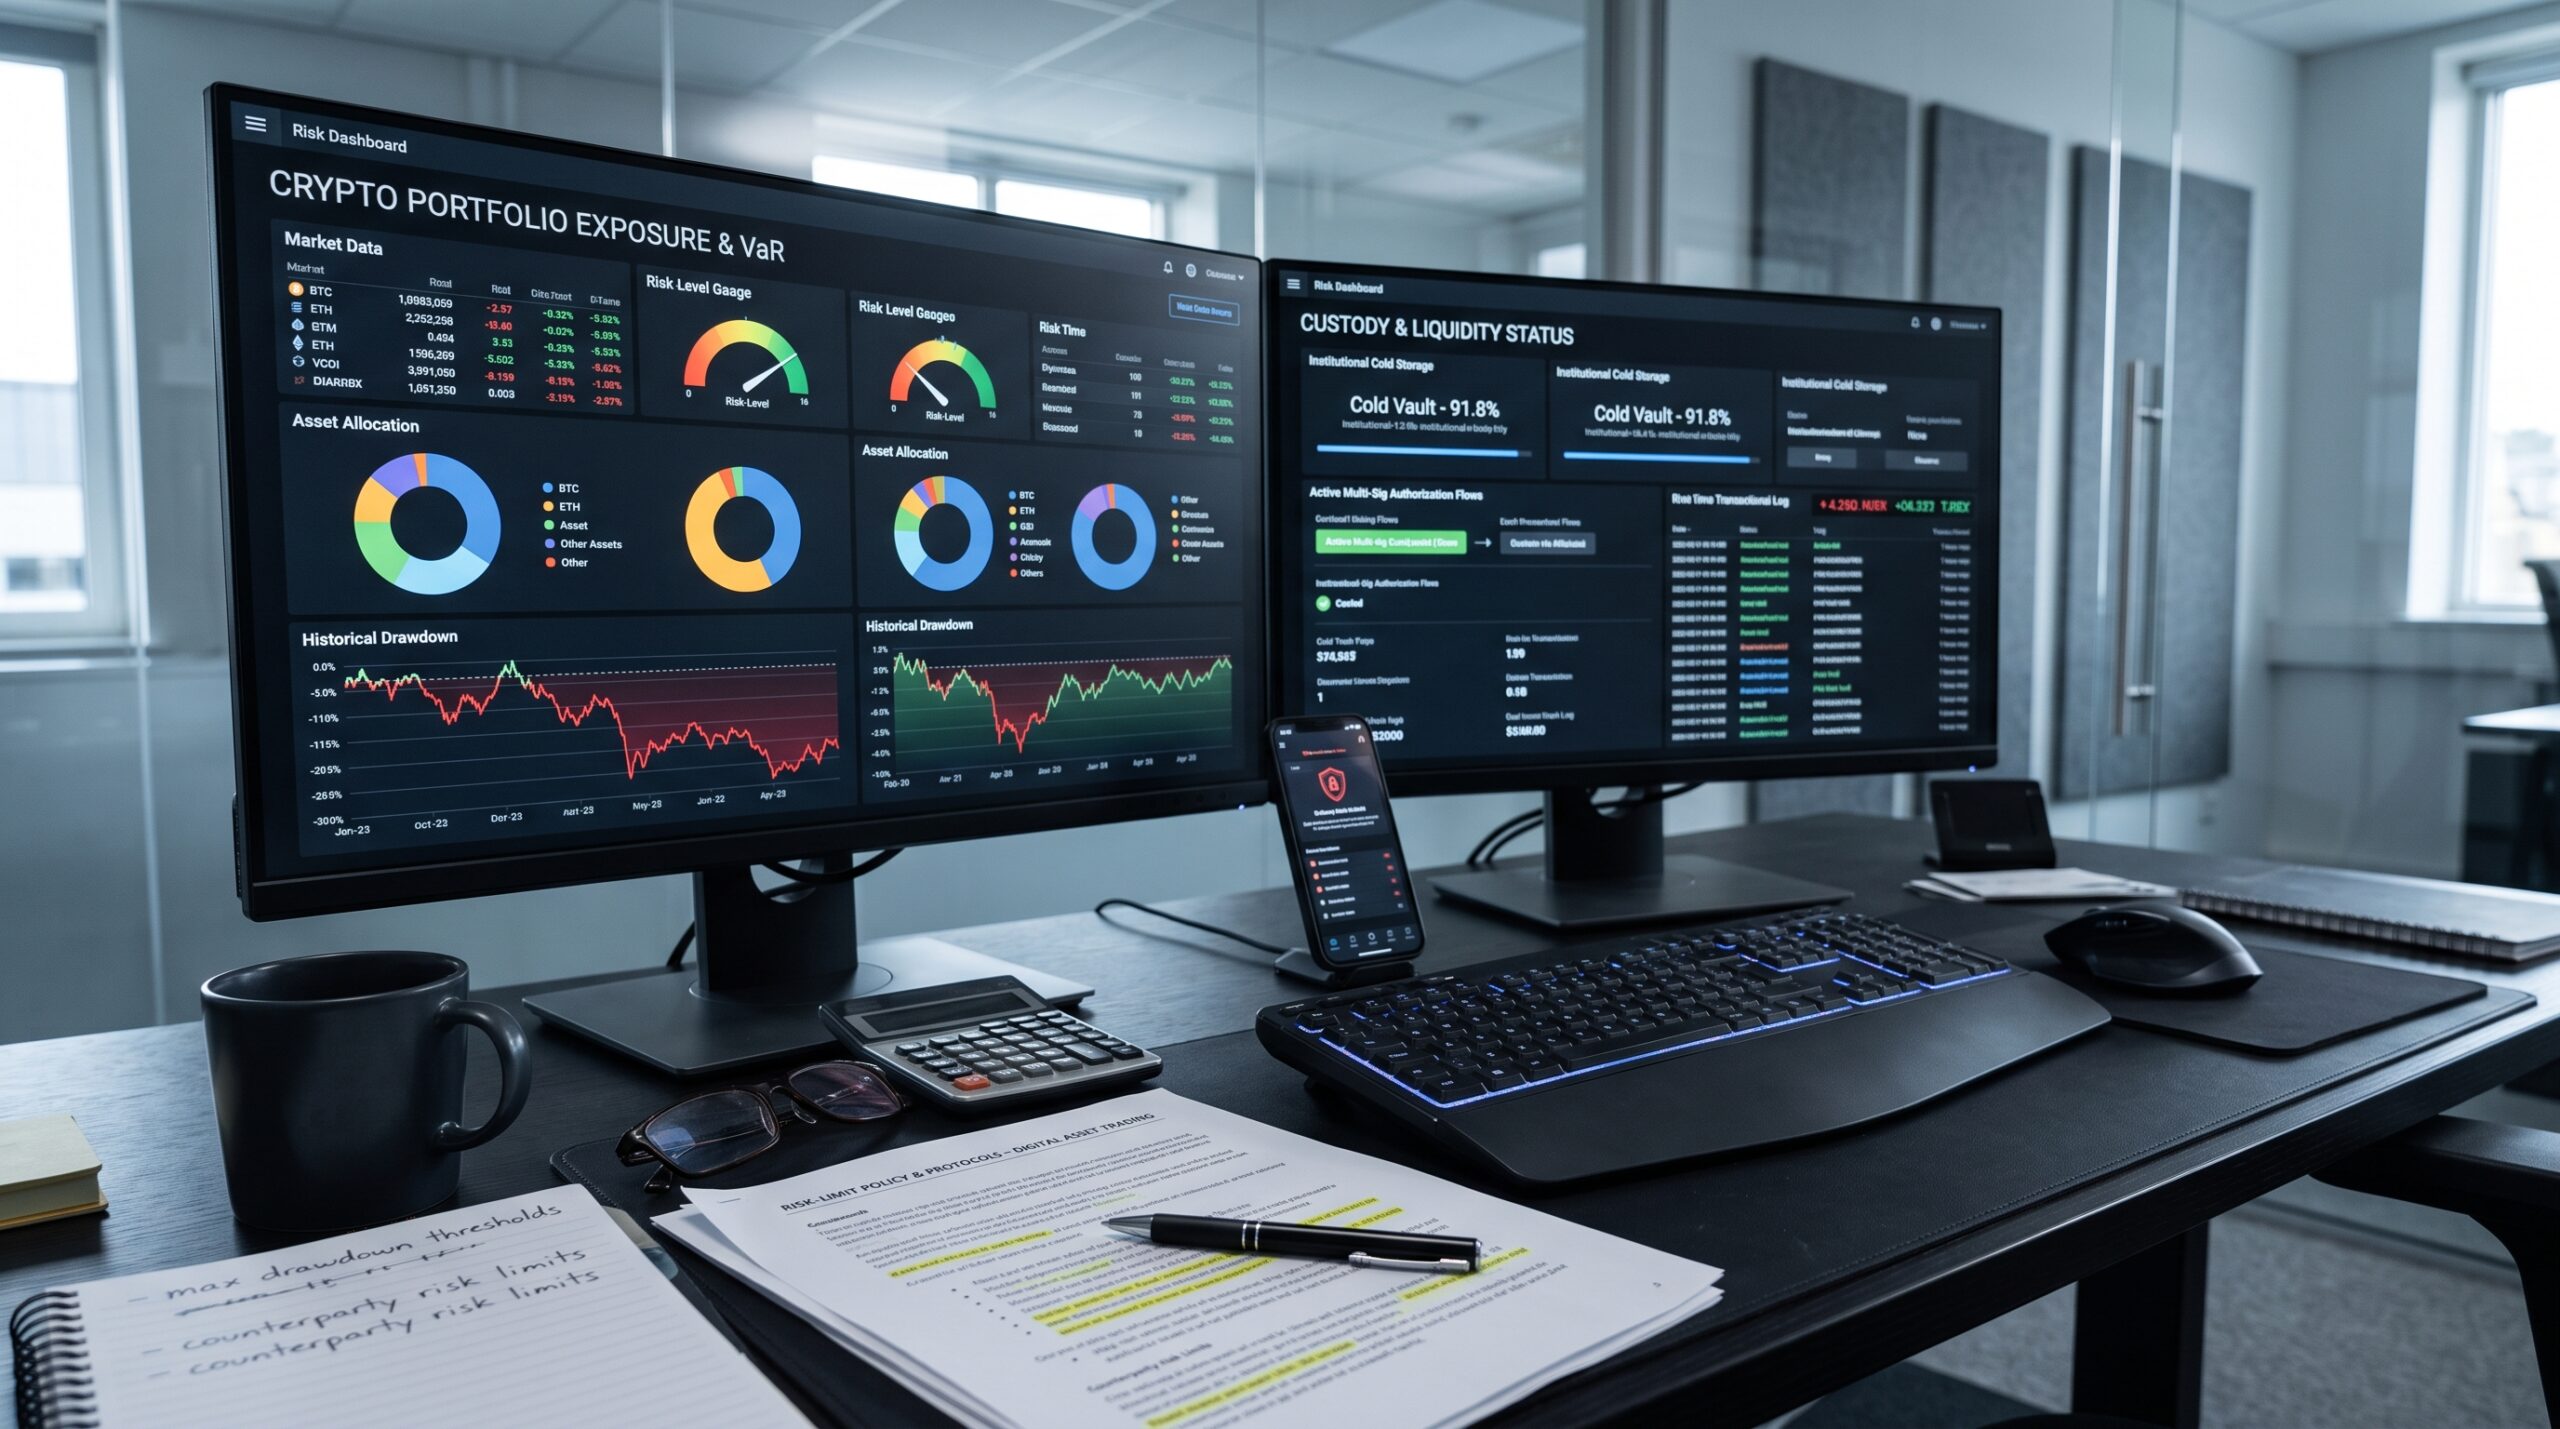
You enter crypto markets with a clear strategy and solid capital, yet a sharp move or operational failure can erase months of careful work. For businesses the difference between a controlled exposure and a damaging loss often comes down to risk management. Price volatility is only one part of the picture. Custody, counterparty, liquidity, and operational risks matter just as much. The firms that remain active through market cycles treat risk controls as the foundation rather than an afterthought.
Define Risk Limits Before Capital Is Deployed
Every serious trading or treasury operation begins with written limits. Set a maximum portfolio allocation to crypto as a percentage of liquid assets or total risk capital. Establish a maximum drawdown level that triggers automatic review or position reduction. Daily and weekly loss limits prevent a single bad period from compounding. These numbers should be approved at the appropriate governance level and reviewed on a fixed schedule. Without pre-committed boundaries, decisions made under stress tend to loosen standards exactly when discipline is most needed.
Separate Custody from Trading Venues
Exchange failures and hacks remain a persistent threat. Businesses that keep large balances on trading platforms expose themselves to platform risk that has nothing to do with market direction. The standard institutional approach is to hold the majority of assets with a qualified, regulated custodian and move only the capital required for active trading to exchange accounts. Cold storage, multi-signature controls, and clear withdrawal policies further reduce the chance of unauthorized movement. Treat custody as a core risk control, not a back-office detail.
Size Positions by Risk, Not by Conviction
A common error is to size a trade according to how strongly the team believes in the thesis. Professional desks size positions according to the impact on overall portfolio risk. A more volatile asset receives a smaller notional allocation so that its contribution to total drawdown stays within limits. Correlation across holdings is monitored; several positions that move together can create unintended concentration. Rebalancing rules and maximum single-asset weights keep the book from drifting into oversized bets.
Manage Liquidity and Exit Planning
Crypto markets can appear deep until you need to exit a large position quickly. Before entering a trade, estimate how many days it would take to unwind under normal and stressed conditions without moving the market excessively. Participation caps relative to average daily volume help keep exits manageable. For less liquid assets the exit plan should be especially conservative. Hypothetical example: a desk limits any single position to a size that can be reduced by 50 percent within three trading days at a predetermined participation rate. The rule forces realistic position sizing from the start.
Control Operational and Counterparty Exposure
Technology failures, key-management errors, and counterparty defaults create losses independent of price. Maintain clear procedures for wallet access, trade confirmation, and reconciliation. Monitor the financial health and concentration of exchanges, prime brokers, and stablecoin issuers you rely on. Diversify critical services where practical and keep documented contingency plans for the sudden loss of a key venue or custodian. Regular audits of processes and access rights catch weaknesses before they become incidents.
Governance, Reporting, and Independent Oversight
Risk management only works when it is visible and enforceable. Independent risk or compliance functions should have authority to challenge position sizes and to enforce limits. Valuation and reporting should follow consistent methods that can be audited. Board or risk-committee reporting should include current exposures, limit utilization, and any breaches or near-breaches. When crypto activity is material, it belongs in the same risk framework that governs other significant financial exposures.
Practical Habits That Compound Over Time
Document every material decision and the risk rationale behind it. Review limits after both strong gains and painful losses; success can breed complacency just as quickly as drawdowns create fear. Keep leverage modest relative to the volatility of the assets involved. Test operational procedures periodically, including withdrawal processes and incident response. The goal is not to eliminate risk but to ensure that no single failure—market, operational, or counterparty—can threaten the broader business.
Crypto trading and treasury activity can serve legitimate business purposes, yet the same markets that offer opportunity can also deliver rapid and severe losses. The organizations that navigate them successfully treat risk management as a continuous discipline: clear limits, segregated custody, risk-based sizing, realistic exit planning, operational controls, and independent oversight. Build these elements before increasing exposure. Review them regularly as market conditions and internal activity evolve. Capital preserved through disciplined risk management remains available for the next opportunity; capital lost to preventable failures does not.
FAQ
What is the most important first step in crypto risk management for a business?
Define and document hard limits on total allocation, drawdown, and single-position size before any capital is deployed.
Why is custody separation so critical?
Keeping the majority of assets with a regulated custodian reduces exposure to exchange failures, hacks, and operational errors on trading platforms.
How should position size be determined?
By the contribution to overall portfolio risk rather than by conviction level or notional preference. More volatile assets typically receive smaller allocations.
What operational risks do businesses often underestimate?
Key management, access controls, reconciliation failures, and concentration with a single venue or service provider.
How often should risk limits be reviewed?
On a fixed schedule and after any material market move, strategy change, or limit breach. Governance bodies should receive regular exposure reports.